On this page
HIPAA (Health Insurance Portability and Accountability Act) establishes national standards for protecting sensitive patient health information. Software systems that handle Protected Health Information (PHI) must comply with HIPAA requirements.
HIPAA Overview
Who Must Comply?
Key Regulations
Security Rule Safeguards
Administrative Safeguards
Physical Safeguards
Technical Safeguards
Software Development Requirements
Access Control Implementation
// Example: Role-based access control for PHI
interface AccessPolicy {
  resource: string;
  actions: ('read' | 'write' | 'delete')[];
  roles: string[];
  conditions?: AccessCondition[];
}

const phiAccessPolicies: AccessPolicy[] = [
  {
    resource: 'patient-records',
    actions: ['read'],
    roles: ['physician', 'nurse', 'medical-assistant'],
    conditions: [
      { type: 'treatment-relationship', required: true },
    ],
  },
  {
    resource: 'patient-records',
    actions: ['read', 'write'],
    roles: ['physician'],
    conditions: [
      { type: 'treatment-relationship', required: true },
      { type: 'break-glass', required: false },
    ],
  },
];

// Enforce minimum necessary access
async function checkAccess(
  user: User,
  resource: string,
  action: string
): Promise<boolean> {
  const policy = findMatchingPolicy(resource, action);
  if (!policy) return false;

  if (!policy.roles.includes(user.role)) return false;

  for (const condition of policy.conditions || []) {
    if (!await evaluateCondition(condition, user, resource)) {
      return false;
    }
  }

  // Log access attempt
  await auditLog.record({
    userId: user.id,
    resource,
    action,
    timestamp: new Date(),
    granted: true,
  });

  return true;
}
Audit Logging
// HIPAA-compliant audit logging
interface AuditEntry {
  timestamp: string;
  userId: string;
  userName: string;
  userRole: string;
  action: 'CREATE' | 'READ' | 'UPDATE' | 'DELETE' | 'EXPORT' | 'PRINT';
  resource: string;
  resourceId: string;
  patientId?: string;
  ipAddress: string;
  userAgent: string;
  outcome: 'SUCCESS' | 'FAILURE' | 'DENIED';
  reason?: string;
  dataAccessed?: string[]; // Fields accessed
}

class HipaaAuditLogger {
  async logAccess(entry: AuditEntry): Promise<void> {
    // Store in immutable audit log
    await this.auditStore.append({
      ...entry,
      id: generateUUID(),
      hash: this.computeHash(entry),
    });

    // Alert on suspicious activity
    if (this.isSuspicious(entry)) {
      await this.alertSecurityTeam(entry);
    }
  }

  private isSuspicious(entry: AuditEntry): boolean {
    return (
      entry.outcome === 'DENIED' ||
      entry.action === 'EXPORT' ||
      this.isAfterHoursAccess(entry) ||
      this.isUnusualVolume(entry)
    );
  }
}
Encryption Requirements
// Data encryption configuration
const encryptionConfig = {
  // At-rest encryption
  atRest: {
    algorithm: 'AES-256-GCM',
    keyManagement: 'AWS KMS', // or HSM
    keyRotation: '90 days',
  },

  // In-transit encryption
  inTransit: {
    protocol: 'TLS 1.3',
    minVersion: 'TLS 1.2',
    cipherSuites: [
      'TLS_AES_256_GCM_SHA384',
      'TLS_CHACHA20_POLY1305_SHA256',
    ],
  },

  // Field-level encryption for highly sensitive fields
  fieldLevel: {
    enabled: true,
    fields: ['ssn', 'medical_record_number', 'diagnosis'],
    algorithm: 'AES-256-GCM',
  },
};
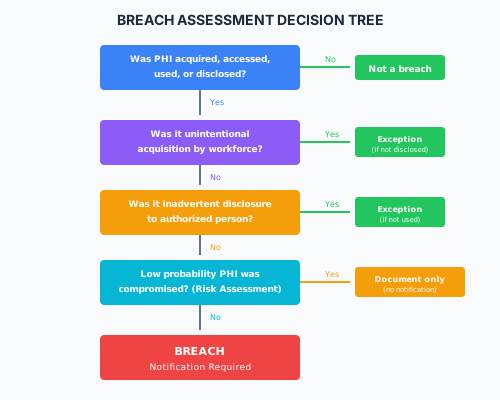
Breach Notification
Breach Assessment
Breach Assessment Decision Tree Notification Timelines
Development Checklist
Design Phase
☐ Identify all PHI data elements☐ Document data flows with PHI☐ Design access control model☐ Plan encryption strategy☐ Design audit logging
Implementation Phase
☐ Implement authentication (MFA recommended)☐ Implement role-based access control☐ Encrypt PHI at rest and in transit☐ Implement comprehensive audit logging☐ Add automatic session timeout☐ Implement secure password policies
Testing Phase
☐ Test access control enforcement☐ Verify encryption implementation☐ Test audit log completeness☐ Conduct security assessment☐ Perform penetration testing
Deployment Phase
☐ Verify production encryption☐ Confirm backup procedures☐ Test disaster recovery☐ Document security controls☐ Train workforce on new systems
Best Practices
Do
Implement minimum necessary access
Use strong authentication (MFA)
Encrypt all PHI at rest and in transit
Log all PHI access
Conduct regular risk assessments
Train workforce on HIPAA requirements
Have breach response procedures ready
Don't
Store PHI in unencrypted form
Allow shared accounts
Log PHI in application logs
Skip security assessments
Ignore audit log alerts
Assume cloud providers are HIPAA compliant by default
Compliance
This section fulfills ISO 13485 requirements for confidential information protection (4.2.4) and customer property protection (7.5.4), and ISO 27001 requirements for information classification (A.5.12), access control (A.5.15), and encryption (A.8.24).
View full compliance matrix